 |
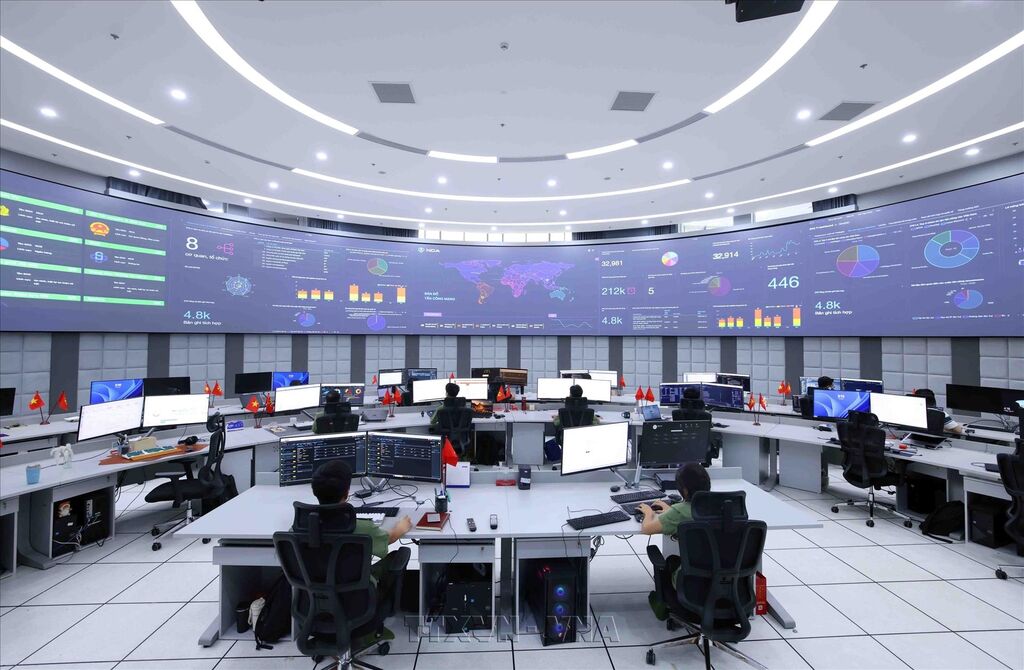
| At the National Cyber Security Center of Vietnam__Photo: VNA |
The draft Law on Data Security (the draft) has been formulated to regulate all aspects of data security, ranging from overarching principles and specific protection mechanisms to resource allocation and state management. Its core principles centre on risk-based security management, protection of data throughout its lifecycle, proactive incident prevention and mitigation, and development of technological infrastructure and human resources.
Defining regulatory scope and avoiding regulatory overlap
A primary objective of the draft is to establish clear regulatory boundaries and rules on the application of laws, ensuring consistency within the broader legal framework. It provides that personal data processing and data subject rights are governed by personal data protection regulations, while data architecture and classification are governed by general data regulations and the security of information systems falls under cybersecurity legislation. In particular, the protection of data security throughout its lifecycle is governed exclusively by the Law on Data Security.
This demarcation prevents organisations and enterprises from facing duplicate procedures for the same management tasks. Furthermore, the draft establishes the principle that an entity facing a particular risk should be subject to only one assessment, appraisal or inspection. This measure aims to reduce compliance costs and facilitate production and business activities for organisations and individuals.
Risk-tiered management aligned with protection needs
A risk-based management approach serves as the cornerstone of the draft, reflecting global legislative trends in recent years. Instead of imposing rigid, uniform rules on all data types, it adjusts compliance obligations according to the actual risks associated with data processing. This proportionate approach seeks to strike a balance between maintaining effective oversight in the face of increasingly sophisticated threats and avoiding blanket controls that waste state resources and impose unnecessary burdens on low-risk operators.
The draft outlines five distinct risk levels, ranging from level 1 (the lowest) to level 5 (the highest), determined by the likelihood of incidents and potential damage to national security, public order and lawful rights. Obligations increase accordingly: levels 1 and 2 involve virtually no administrative procedures, while level 3 and higher require impact assessments and periodic audits. At levels 4 and 5, mandatory security appraisal is integrated with broader cybersecurity assessments before systems are officially put into operation. Importantly, these levels are independent of general data classification and do not alter lawful ownership or management rights over data.
Lifecycle protection and cross-border control
The draft requires security measures throughout the data lifecycle, from collection, storage, processing and transmission to eventual deletion or destruction. It introduces differentiated controls for cross-border data processing proportionate to the level of risk in order to safeguard national data sovereignty. Additionally, the framework protects domestic entities against unauthorised requests for data made directly from overseas, in line with principles of national sovereignty and international judicial assistance.
Proactive incident response and safeguarding rights
The draft establishes mechanisms for the proactive prevention, monitoring and containment of serious data security incidents, providing the State with tools for rapid response. Measures restricting individual rights are subject to strict conditions: they must have a clear legal basis, comply with the principle of least restriction, be subject to specified time limits and remain under oversight. Affected parties retain the right to submit petitions, lodge complaints, initiate lawsuits and seek compensation for unlawful measures.
Securing new technologies, artificial intelligence, and supply chains
Emerging technologies and artificial intelligence (AI), entities developing high-risk AI systems that process data must incorporate security measures from the design stage, ensuring that data is lawfully sourced and its integrity maintained. Assessments will be integrated into existing AI risk assessment procedures without requiring separate dossiers or independent appraisals. To protect corporate trade secrets, authorities are expressly prohibited from demanding source code or model weights except in cases involving criminal investigations.
Furthermore, data controllers will be required to assess third-party risks, restrict remote access, include confidentiality clauses in relevant agreements and retain the right to revoke access privileges when vulnerabilities are detected.
Fostering infrastructure, technology, and human resources
The State will prioritise the development of sovereign cloud computing, secure environmentally friendly data centres, and offer tax incentives for research into data security and post-quantum cryptography. Small- and medium-sized enterprises and startups will receive support through self-assessment tools and shared services. Finally, the draft prohibits granting exclusive rights to any single product or supplier, with a view to ensuring competition in the market.- (VLLF)