 |
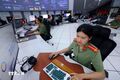
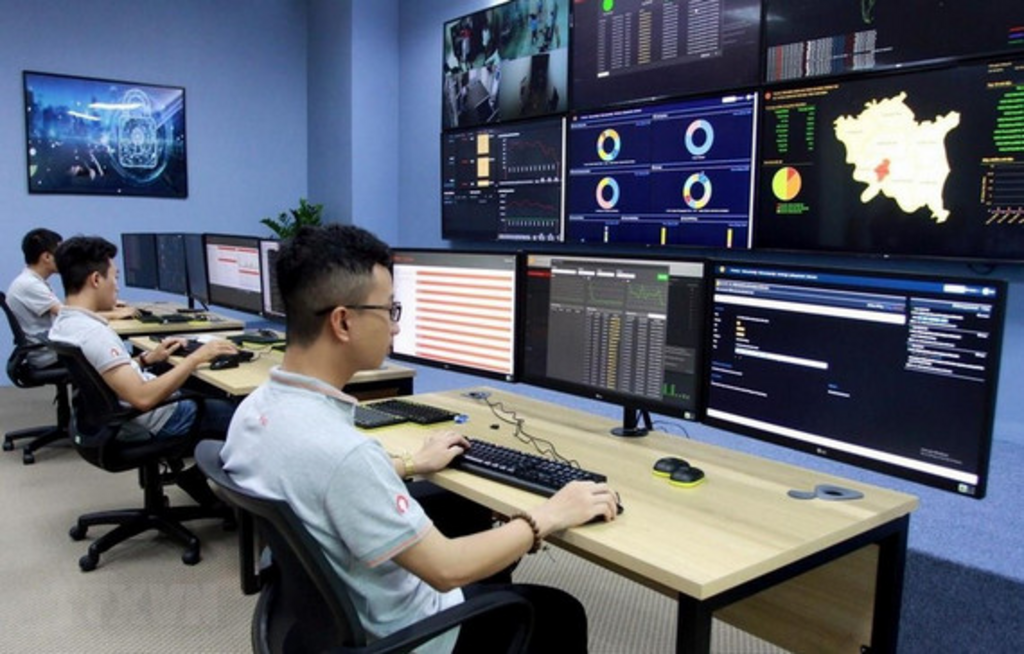
| Inside a cybersecurity operations center__Photo: VNA |
The Prime Minister has approved the introduction of a national Cybersecurity Assurance Index comprising 29 criteria included in three criterion groups to evaluate cybersecurity performance among ministries, government agencies and local authorities.
The Index is designed to provide a standardised framework for assessing cybersecurity preparedness and protection measures, supporting state management and policy making concerning national cybersecurity.
Under Decision 1964/QD-TTg dated October 12, 2026, the Index will be implemented on a pilot basis during 2027–28, with official assessments envisaged from 2029, subject to the Prime Minister's approval.
Specifically, criteria in the first two assessment groups will be used to serve calculation of the Index, while those in the third group will provide information to support management and decision-making.
The first group, covering general assessment criteria, applies to all information systems and their managing entities. It consists of two sub-criteria: compliance with requirements for information systems’ risk level classification dossiers, and compliance with risk level-based cybersecurity assurance plans.
The second group comprises 18 specific assessment criteria applicable to information systems classified at level 3 or higher level and their managing entities.
These criteria cover cybersecurity risk management; hardware, software and information asset management; secure configuration of hardware and software; user account and access rights management; vulnerability and cybersecurity log management; protection of web browsers and email services; malware prevention; data backup and recovery; network infrastructure management; and cybersecurity defence monitoring.
Other criteria address personnel responsible for system operation, administration and cybersecurity protection; management of product and service providers; secure application development; cybersecurity incident response governance; and cybersecurity inspection management.
The third group, which applies to all information systems and their managing entities, consists of nine sub-criteria intended to support management and decision-making by providing quantitative information on cybersecurity risks and incidents and their consequences.
These criteria measure the proportion of risk mitigation measures implemented on schedule, the percentage of cybersecurity incidents promptly controlled and resolved, and the number of serious cybersecurity incidents.
Other criteria cover the number of incidents involving the disclosure of state secrets in cyberspace, the number of classified state documents published or transmitted online due to cybersecurity incidents, and ratio of financial losses caused by cybersecurity incidents to the total budgets allocated to cybersecurity assurance.
During the 2027–28 pilot phase, ministries, government agencies and local authorities will assess information systems under their management in accordance with the Index's structure, principles and methodologies set out in the appendices accompanying the decision.
Assessments will be conducted under the guidance of the Ministry of Public Security, which acts as the standing agency responsible for monitoring, evaluating and summarising annual evaluation results.
A preliminary review of the pilot implementation is scheduled for the second quarter of 2028. The findings will provide a basis for reviewing and refining the Index before its official application.
Assessment results from the pilot phase will not be used to determine emulation and commendation awards or evaluate the performance of ministries, ministerial-level agencies and provincial-level People's Committees.
Based on the review's findings, the Ministry of Public Security will propose to the Prime Minister for consideration and decision the Index's official implementation for 2029–30 and its application in subsequent years, taking into account emerging technological trends and national cybersecurity governance requirements.
Once officially implemented, i.e., from 2029 onwards, assessment results will be reviewed and submitted to the Prime Minister, with rankings to be published annually before May every year in accordance with regulations.
Official assessment results will serve as an important reference for performing state management and making macroeconomic policies and strategies on national cybersecurity.- (VLLF)